

From Ball And Chain To Growth Lever
I entered startup land in 1998.
Security at that time felt like a ball and chain you carried everywhere.
SSAE16. HIPAA. Internal standards nobody outside the audit room understood.
Every serious deal came with a spreadsheet full of controls that stretched for thousands of lines.
My title said “Head of Technology.”
Reality added a long, invisible subtitle that included architecture, production, vendor integrations, data flows, and every question that began with “are we secure.”
If it plugged into a wall, I was responsible for it.
We built and ran our own infrastructure.
We picked hardware, racks, firewalls, backup devices.
We patched operating systems, tuned databases, and managed cages in data centers.
Then SaaS arrived.
Multi-tenant architectures became the norm.
In 2009, I spent a lot of time explaining to serious buyers that their “instance” of our application lived inside a shared environment. At the same time, many still asked for their own physical servers, storage arrays, and even their own locked cage in a colo for that application. The architecture lived in a cloud-shaped world. The expectations still lived in a world of serial numbers on metal and physical keys on a ring.
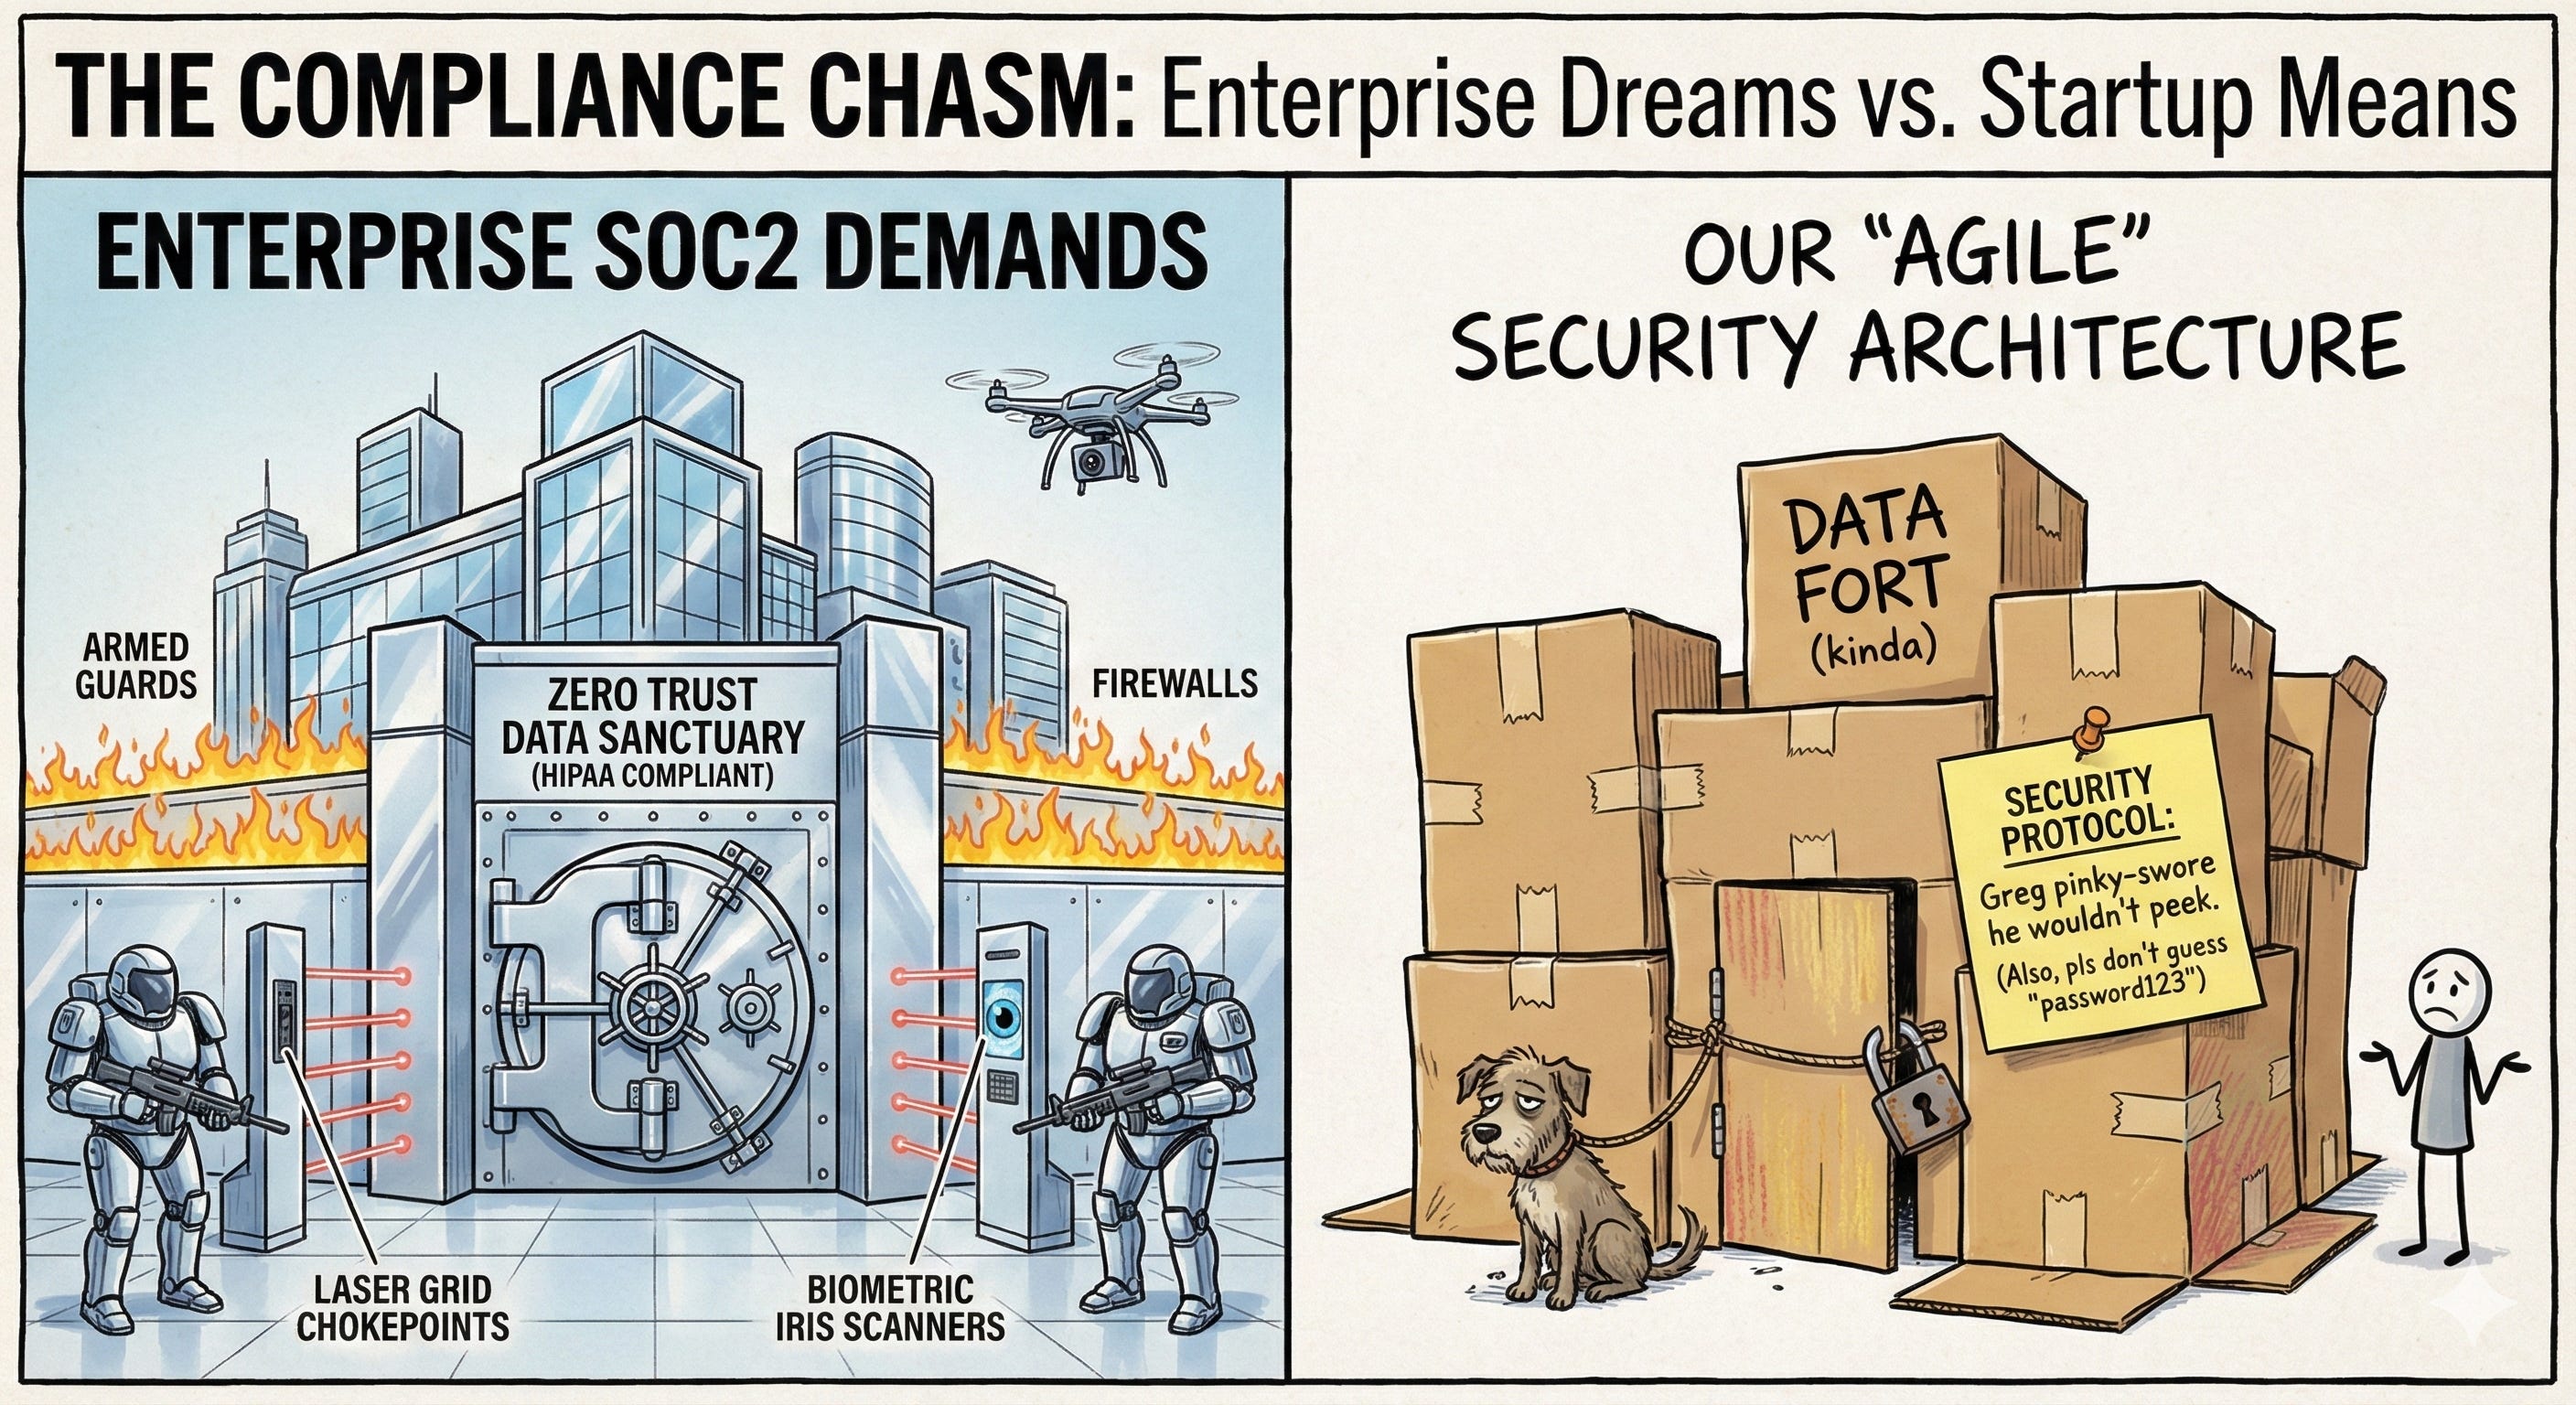
Enterprise sales cycles evolved around one person: the security adjudicator.
This individual reviewed every row in those spreadsheets.
This individual compared our answers to their standards and their scars.
This individual carried the weight of the decision when they signed next to our logo.
My role on those deals became simple:
Earn that person’s confidence and give them a story they could defend inside their own company.
Fast forward.
A founder sends me a message about SOC 2 today:
Vanta scope: $18,000/year for the platform, $5,000 USD for the audit.
Total: $26,000 USD, paid every year to keep the accreditation alive.
That level of spend feels reasonable for a funded scale-up.
For a bootstrapped or early-seed company, it feels like a senior hire.
At the same time, the landscape created new leverage for founders:
Free or near-free SOC 2 readiness platforms exist for small startups. They generate policies, connect to your cloud, and produce a live view of controls.
Startup-focused providers bundle automation, penetration tests, and audits into fixed-fee packages in the five to eight thousand dollar range.
Boutique SOC 2 auditors agree to milestone-based payment structures when a founder arrives with real preparation and a real enterprise deal on the table.
The big unlock sits in one insight:
You can reach SOC 2 Type I on a shoestring by sequencing the work around a specific enterprise deal, leaning on a free readiness platform for posture analysis, and structuring the audit fee so most of the cost rides on closed revenue.
This guide exists as a Growth by Design playbook for that path.
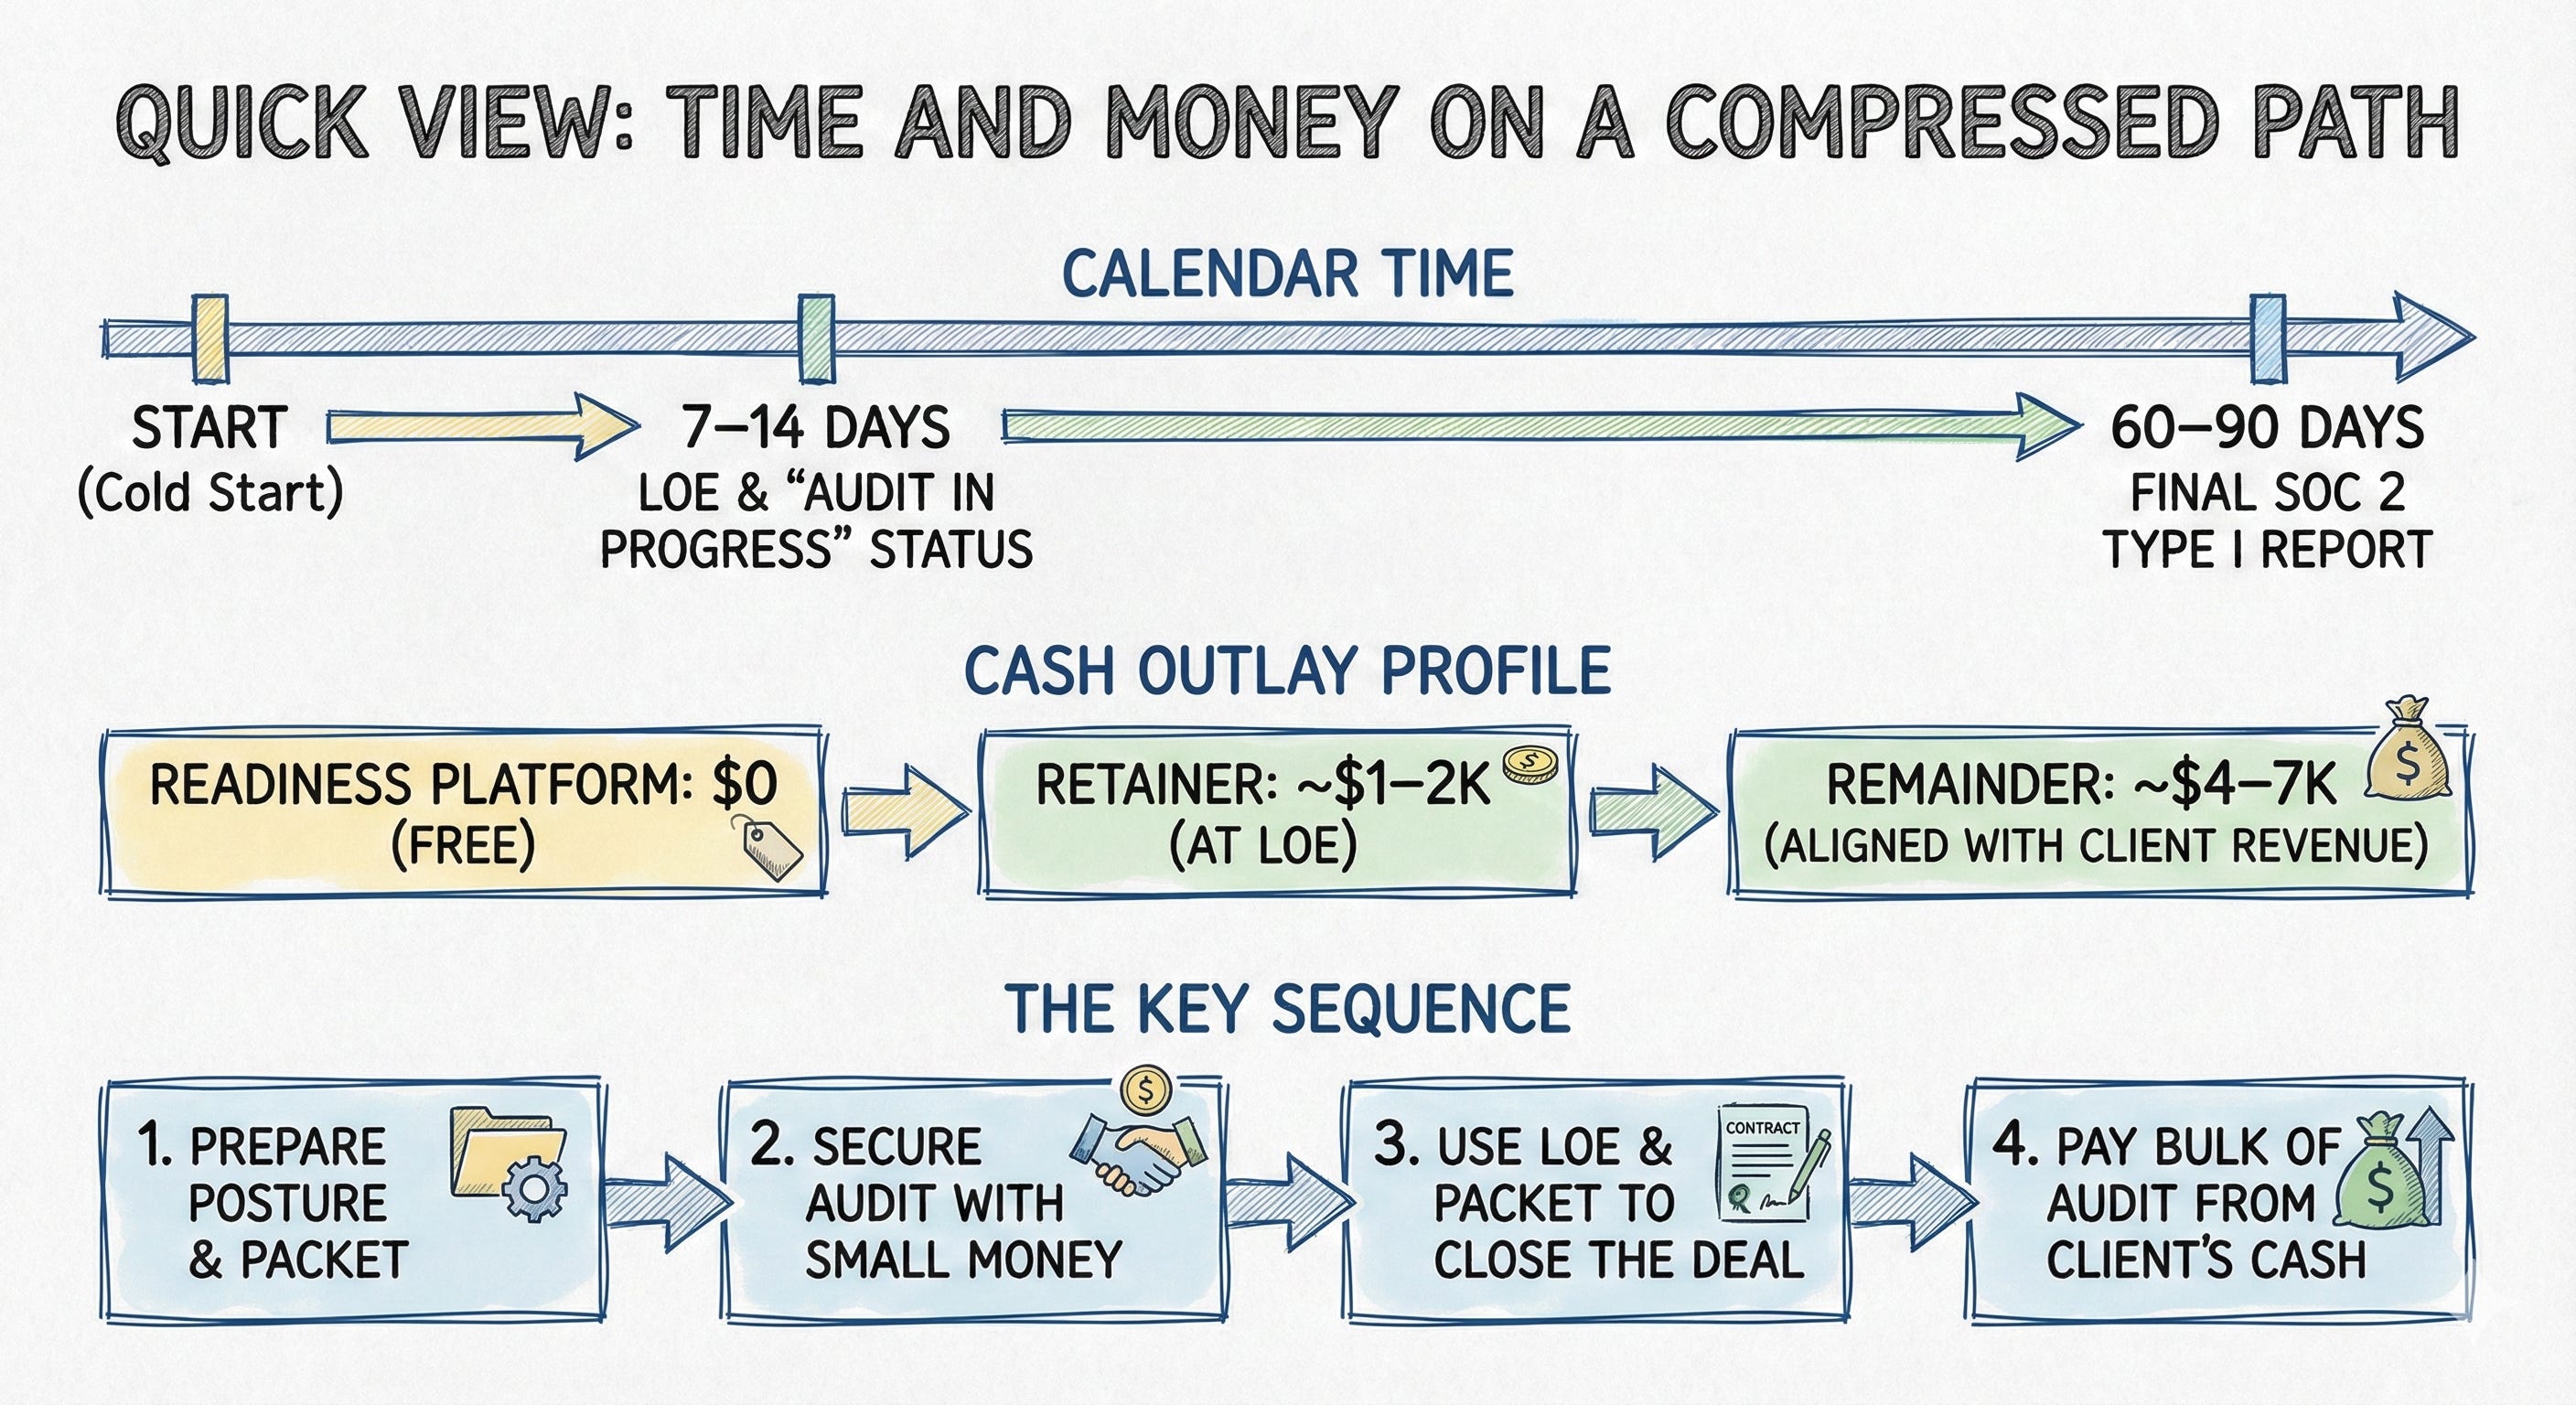
The core idea looks like this:
Use a free SOC 2 readiness platform to perform posture analysis and generate policies.
Aim for a SOC 2 Type I report with a tight, revenue-aligned scope.
Engage a boutique auditor with a small retainer and a “pay the rest when the draft report lands” structure.
Use the signed Letter of Engagement plus your security packet to satisfy the client’s security team and close the deal during the audit window.
Pay the majority of the audit fee from the client’s money, not from savings.
You treat SOC 2 as a growth project, not as an abstract compliance goal.
The rest of this guide explains how to do this in a structured way.
Part 1 gives you the quick-start shorthand: steps, costs, and time.
Parts 2 through 5 expand each step into detailed instructions, scripts, and checklists.
Use this as a working manual with your leadership team.
Anchor it around a real logo that already asks about SOC 2.
Turn security from a blocker into a lever.
Part 1: SOC 2 On A Shoestring – Shorthand Playbook
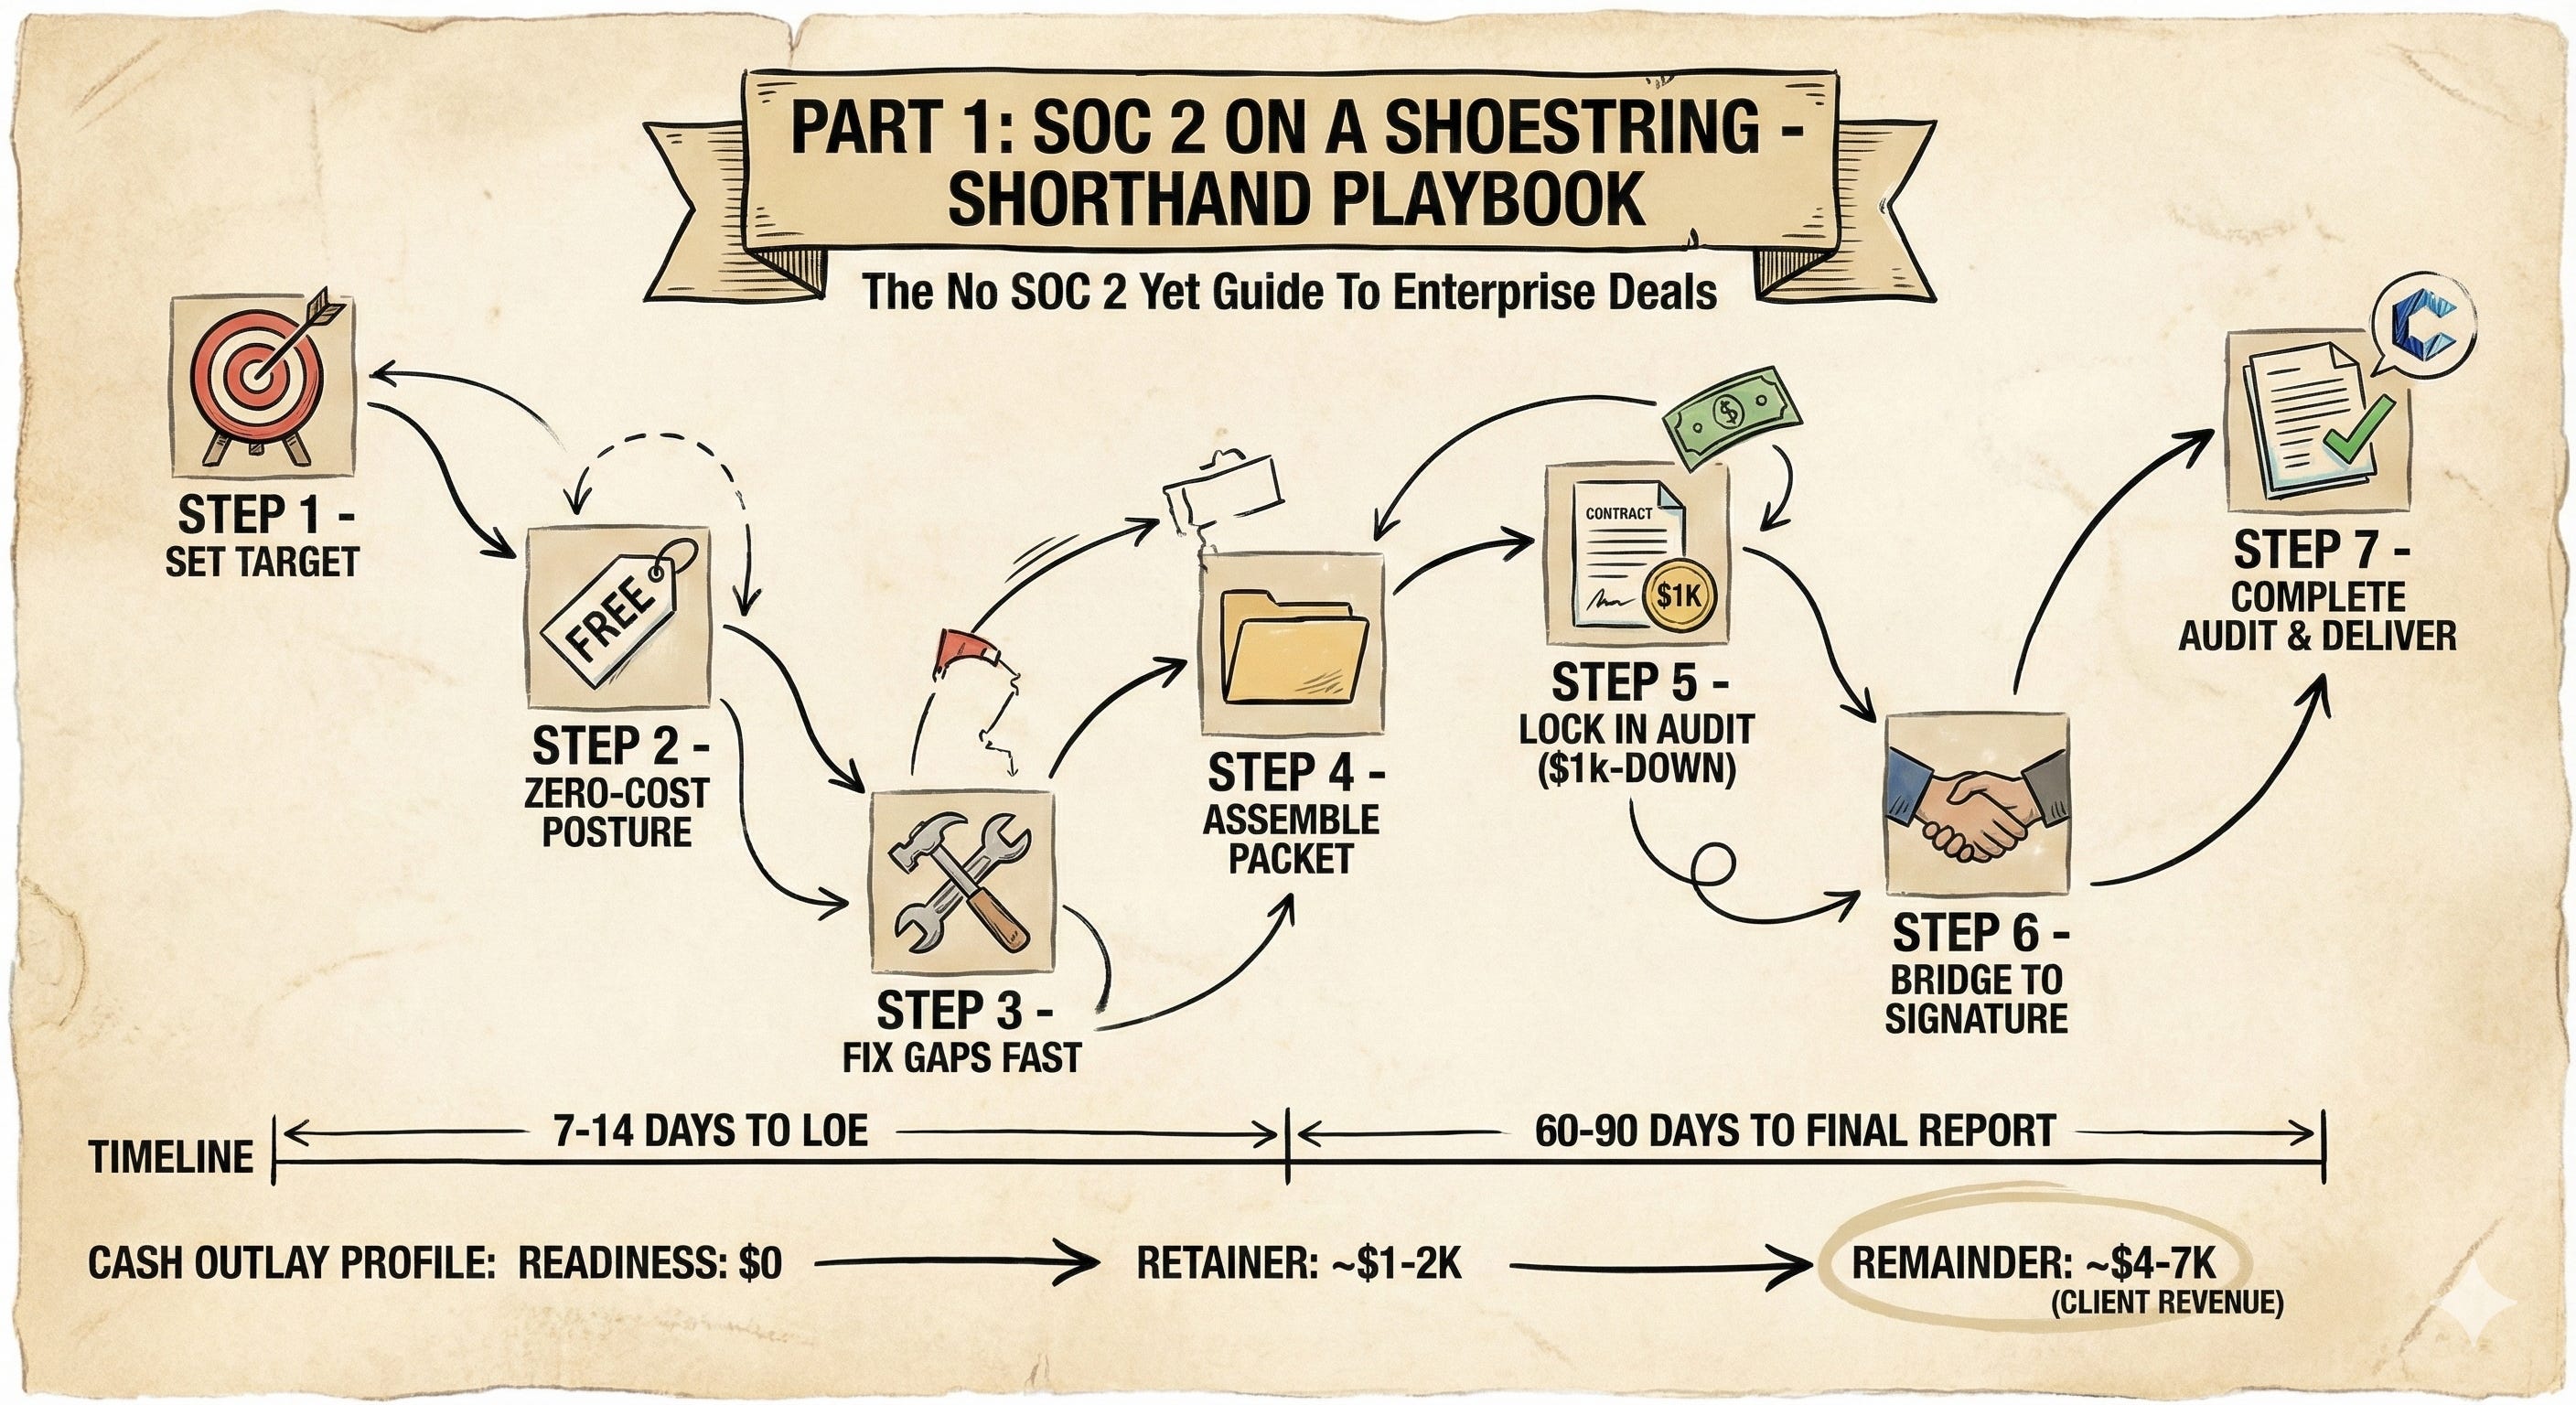
This section gives you the fast overview:
What to do
In what order
Rough cash required
Rough time required
Treat it as the front page of your SOC 2 plan.
Parts 2 onward expand each step.
